In August 2026, details began to come to light regarding the ChainDrop npm supply-chain compromise, in which malicious package releases searched developer workstations and CI/CD environments for credentials that could publish packages or reach source control and cloud infrastructure. Once stolen, those identities could help the malware spread into more packages and repositories, enabling still deeper reach into the development environment.
A developer’s laptop is not just another client device in that chain. It can be where source code is cloned, cloud sessions are opened, and package or build credentials are used.
Phones and tablets offer a quieter route in. From an iPad, a developer can approve a pull request, open a cloud console, or run an SSH client. Often that happens outside the checks laptops go through.
A junior engineer faces the same exposure as a senior developer who has access across several repositories and cloud accounts. Both usually need working credentials. An attacker who compromises an endpoint gains several routes into the same development environment. And that’s before they’ve exploited a separate server or application.
This is where mobile device management (MDM) fits into zero-trust design. Enrollment alone shouldn’t give a device a permanent pass. That goes for laptops, smartphones, and tablets alike. Say a developer wants to access a production console or a private repository. MDM can help check whether the machine is still in the state that access requires.
This leaves us with four practical questions. What can MDM verify? How fast does a developer laptop drift? How much control is reasonable on BYOD? And what should happen when a check fails?
A Managed Device Is Not a Trusted Session
Mobile device management matters most when its posture checks affect a real action. Before a developer opens a production console, the laptop might need encryption on, a current enough OS, and endpoint protection still reporting. Public documentation doesn’t require the same level of control.
Passing those checks still says little about what happens next. A fully patched, encrypted laptop may carry production credentials, an exposed token, or a malicious extension. ChainDrop is a case in point. The worm ran the moment a developer installed an affected package, on machines that could easily have passed every posture check. Device posture narrows uncertainty, but it does not describe everything happening inside the session.
MDM is strongest at configuration questions. Is the device patched? Is encryption on? Is required software still reporting healthy? Other controls pick up from there. Endpoint detection watches behavior, identity controls evaluate the user and session, and repository or cloud permissions determine what that session can reach.
A device can be impeccably configured while an access token has already been copied into the wrong terminal session. That is the useful boundary for MDM in zero trust. Its posture signals should influence access, with stricter requirements for more sensitive resources.
Developer Laptops Drift by Design
Developer machines change during the workday. A project may require a new Node.js runtime, a Docker image, or a local database that was not there yesterday. A developer may also need administrator rights to debug something that a standard corporate laptop would never allow. Policies written for a relatively fixed office PC can become noise very quickly.
A laptop can pass its checks at 9 a.m. and look different by lunch. An OS update may be postponed because a build is running. The endpoint agent may stop reporting after a reboot.
Even a tool you install for one task can change what’s running on the machine. Certifying a laptop once and then forgetting about it won’t get the job done. Posture needs rechecking as the machine changes. Policy, meanwhile, has to absorb normal developer work without flagging every routine change.
Consider a postponed OS update. A grace period helps here, because the developer gets to finish a running build before that update counts against access. Same with debugging. Admin elevation with a time limit can cover the session, and no permanent local admin rights get left behind. And an endpoint agent that stops reporting should be treated as a posture signal in its own right, not as missing data.
BYOD Shrinks the Management Boundary
Company ownership over hardware gives IT broad authority over configuration and software, as well as the ability to support or wipe the machine. A personal device is different. The employer has a security interest in the work data, but the rest of the machine may belong entirely to the employee or contractor.
Apple’s User Enrollment and Android’s Work Profile are built around this limitation, separating work-related management from personal content. This narrows the question: does IT need the whole device, or only enough control to verify posture and protect work data?
Consider a contractor who needs access to Git repositories and a test environment for three months, along with ordinary collaboration tools. Full administrative control over the contractor’s personal laptop may be disproportionate to that access. A work profile or isolated workspace may cover the actual risk with less privacy and support overhead.
MDM still has a role here, particularly where the platform supports limited enrollment. It simply should not be the automatic response to every unmanaged endpoint.
Tie MDM to Access, Not Ownership
Ownership helps set the boundary, but it should not decide access by itself. A company laptop can accept much tighter management than a contractor’s MacBook. Even so, the useful question remains what that machine is trying to open. A Git repository, an internal wiki, and a production console do not need identical rules.
A managed developer laptop might be allowed into internal Git and CI/CD only while it is patched, encrypted, and reporting healthy endpoint protection. Production infrastructure could add stronger authentication and shorter-lived credentials. A personal device might be limited to documentation or a contained development workspace, while production administration stays on fully managed machines.
In practice, the pieces meet at the access request. Identity confirms the developer. MDM reports whether the laptop still meets the required baseline. A conditional access layer then decides whether that combination is enough for the repository, build system, or cloud console being opened.
Policy can also change without rebuilding the developer environment. If a newly disclosed vulnerability makes one OS version unacceptable, the organization can tighten the posture requirement for sensitive resources. If a contractor leaves, identity access can be revoked even though IT never owned the laptop.
Posture Changes Access Decisions
Start with the resource and work backward. Pick a real access path and decide what should happen when the laptop stops meeting policy. If endpoint protection stops reporting, should production access close? If the OS falls below the approved version, should the developer still reach the same private repositories? If a personal device cannot meet the full baseline, which lower-risk tools should remain available?
MDM earns its place when the answers change what the device can actually reach. If nothing changes, the posture data is mostly inventory. In zero trust, posture should impact access.
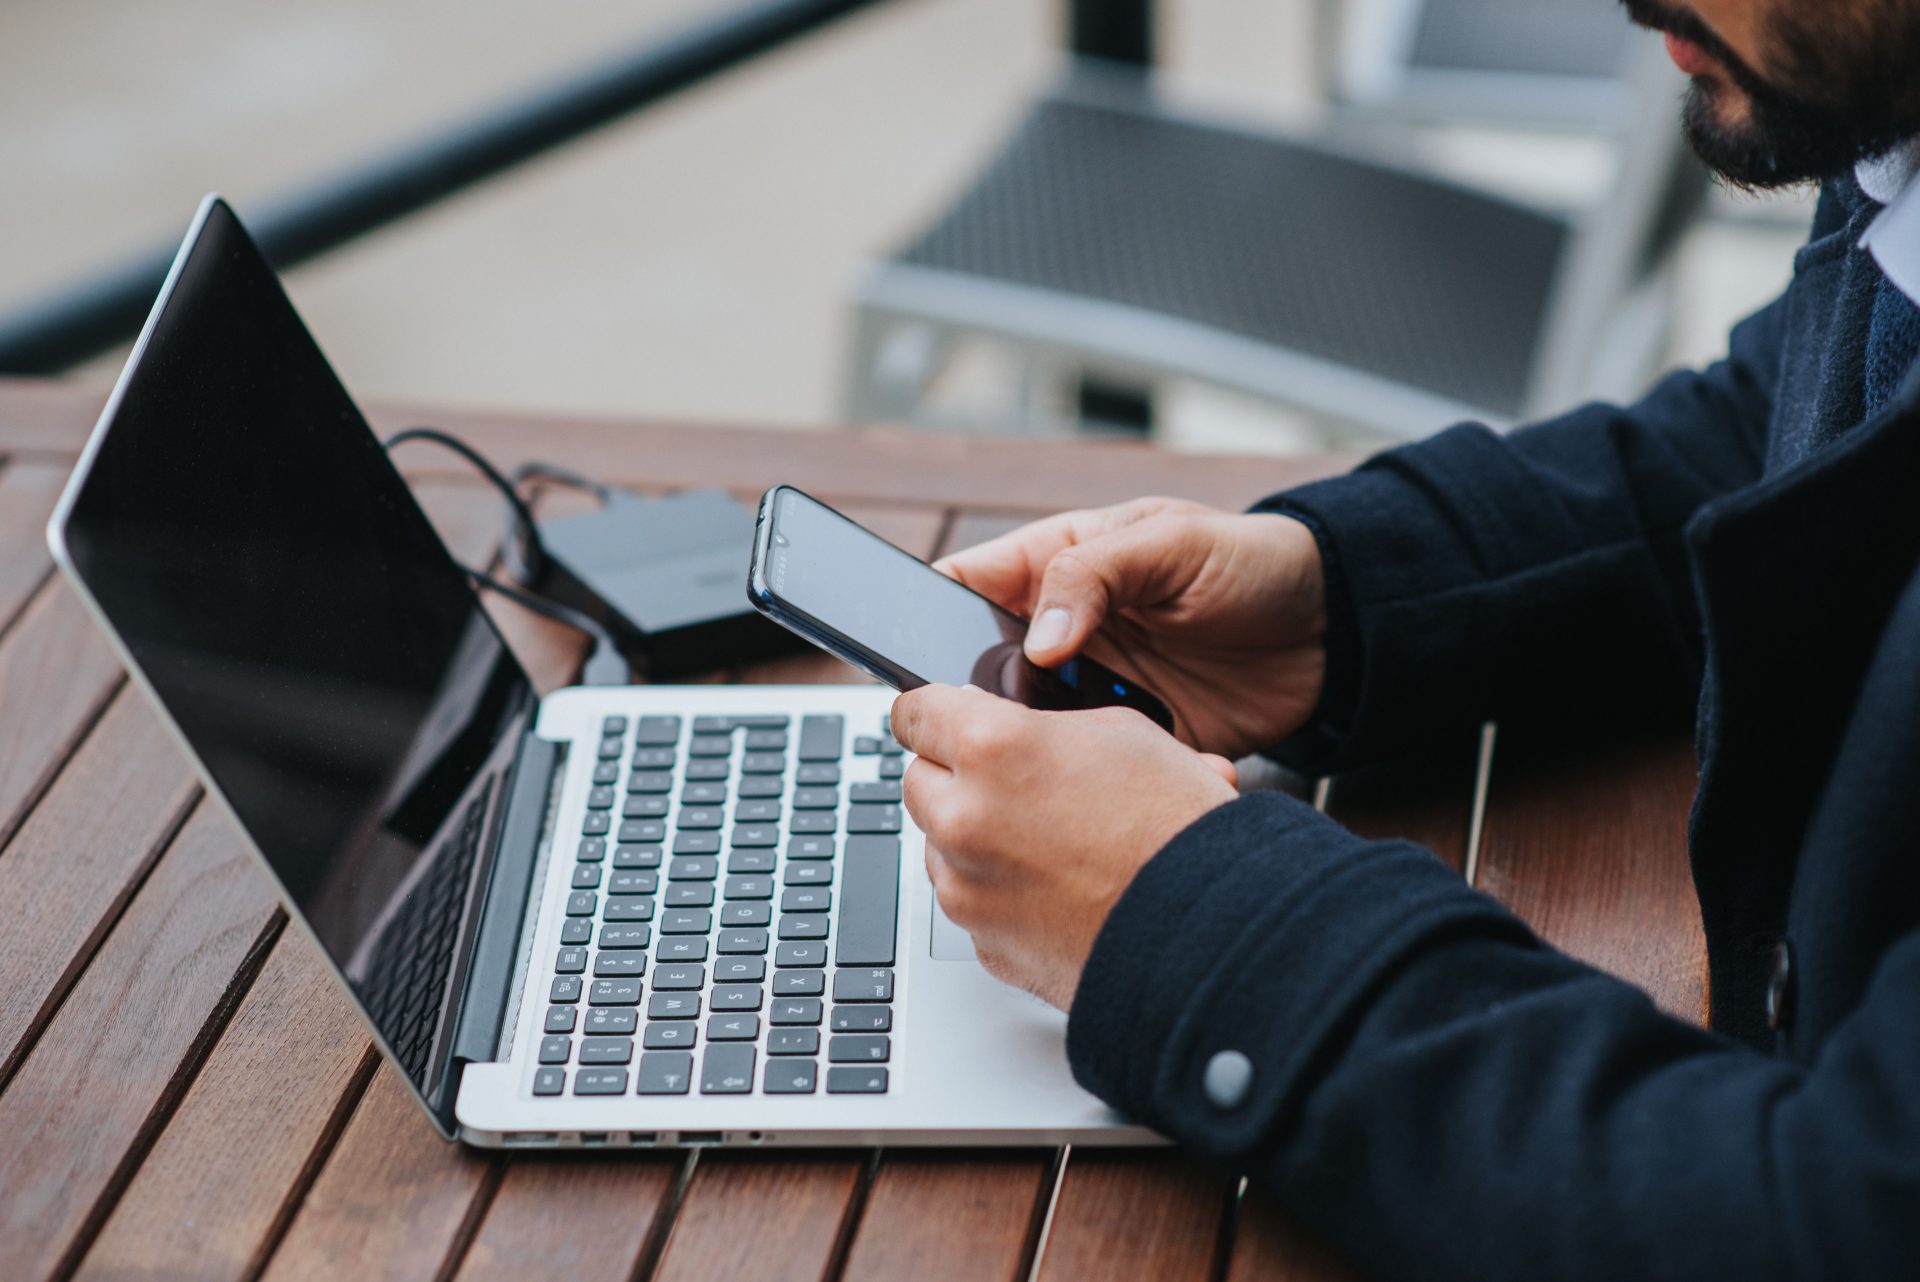
Photo by Anete Lusina: Pexels
Marcus Whitfield writes about developer tools, programming languages, and the software trends shaping how engineers build. Before joining DevX, he spent five years as a full-stack developer and two more running a small dev-tools newsletter that topped 10,000 subscribers.