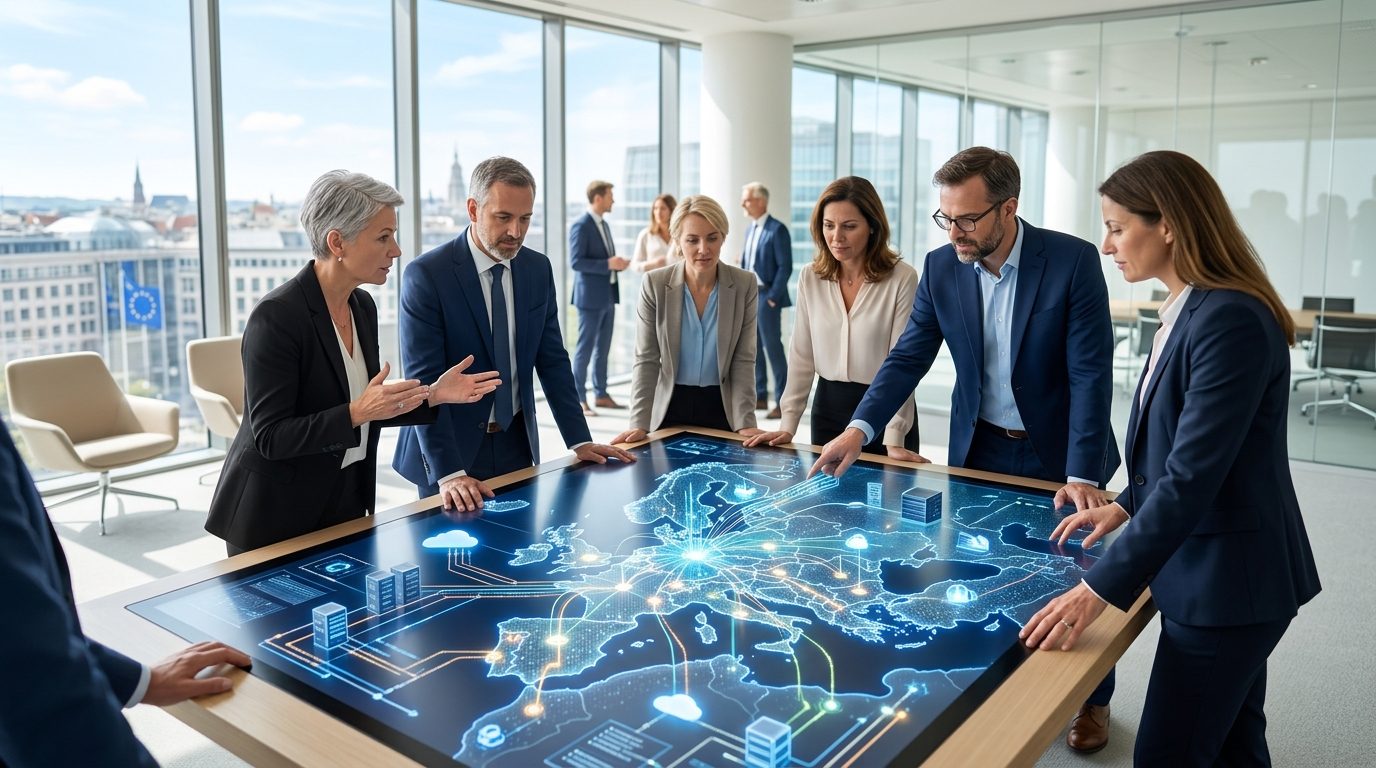
European policymakers are shifting the debate over digital control from technology ownership to practical authority over data, infrastructure, access and daily operations.
The emerging approach could shape how governments and companies select cloud services, manage sensitive information and assess dependence on foreign technology providers. It also offers a more measurable view of digital sovereignty, a long-running priority across the European Union.
Control Matters More Than Full Ownership
Owning every part of a technology system has often been treated as the clearest form of independence. Yet modern digital services rely on suppliers, data centers, software developers and network operators spread across several countries.
That structure makes full ownership difficult and, in many cases, costly. European policy discussions are placing greater weight on whether an organization can prove control over five areas:
- Data storage, use and deletion
- Physical and cloud infrastructure
- User and administrator access
- Operational decisions and system changes
- Data transfers between services and countries
“Control is demonstrated through governance over data, infrastructure, access, operational authority and data flows, rather than through ownership of the full technology stack alone.”
This standard asks a practical question. If a government agency or business does not own the entire system, can it still decide who uses the data, where it moves and how the service operates?
European Rules Provide Policy Context
The discussion fits with Europe’s broader effort to set stricter rules for data and digital services. The General Data Protection Regulation established strong duties for processing personal information. It also placed limits on transferring that information outside Europe.
Newer EU measures have widened the focus. The Data Governance Act addresses trusted data sharing. The Data Act sets rules for access to connected-device data and switching between cloud providers. The NIS2 Directive raises cybersecurity duties for many essential and important organizations.
These measures do not require every organization to build and own its entire technology system. Instead, they rely heavily on contracts, access controls, audit records, security procedures and defined legal responsibilities.
The EU has also promoted regional cloud and data projects. Such efforts reflect concern about dependence on a small group of large providers, many headquartered outside Europe.
A Test for Cloud Contracts
A control-based standard may change technology purchasing. Buyers could give greater attention to audit rights, encryption keys, administrator privileges and plans for leaving a provider.
Data location alone may not settle the issue. Information stored in a European data center could still be managed through tools or staff located elsewhere. Legal demands from another jurisdiction may also affect access.
At the same time, requiring local ownership of every technical layer could reduce competition and increase costs. Smaller European suppliers may also depend on global hardware, software or network services.
A balanced assessment would therefore examine actual decision-making authority instead of relying only on a provider’s headquarters or the location of its servers.
Proof Will Define the Standard
The main challenge is turning the idea of control into evidence. Organizations may need clear records showing who can enter systems, approve changes, retrieve data and authorize international transfers.
Independent audits and transparent contracts could help. Exit testing may be equally important because control is limited if customers cannot move their information to another service within a reasonable period.
Europe’s policy direction suggests that digital independence will not require complete ownership in every case. It will require demonstrable authority over sensitive operations and information.
The next issue to watch is how regulators define acceptable proof. Clear standards could give buyers more confidence and suppliers more certainty. Vague requirements, however, could produce conflicting national rules, higher compliance costs and disputes over what meaningful control actually requires.

Senior Software Engineer with a passion for building practical, user-centric applications. He specializes in full-stack development with a strong focus on crafting elegant, performant interfaces and scalable backend solutions. With experience leading teams and delivering robust, end-to-end products, he thrives on solving complex problems through clean and efficient code.